Comp AI, an emerging leader in the cybersecurity and compliance sector, officially announced on Thursday the successful closure of a $34 million Series A funding round. The significant investment was spearheaded by prominent venture capital firms Roo Capital and Grand Ventures, signaling strong market confidence in the startup’s innovative approach to automating complex security and compliance workflows through advanced artificial intelligence. This latest injection of capital brings Comp AI’s total funding to date to $37.5 million, positioning the company for accelerated product development and market expansion in a rapidly evolving digital landscape.
The funding arrives at a critical juncture for businesses grappling with an increasingly stringent regulatory environment and the burgeoning security challenges introduced by the widespread adoption of AI technologies. Comp AI’s core mission is to alleviate the burden of tedious security and compliance tasks by leveraging an agentic AI platform designed to automate processes such as policy generation, evidence collection for audits, and continuous compliance monitoring. This strategic investment underscores the growing demand for intelligent automation solutions that can help organizations navigate the complexities of modern cybersecurity and regulatory adherence, especially as the "agentic era" of AI begins to reshape enterprise operations.
The Genesis of Innovation: Lessons from a Prior Venture
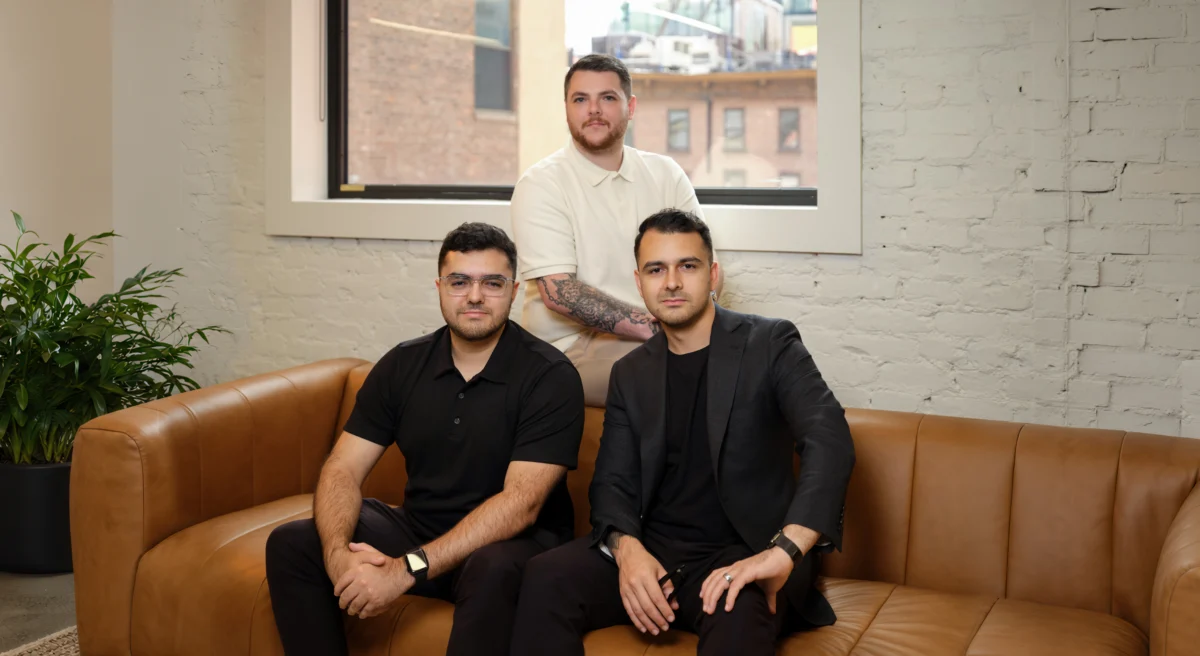
Comp AI was founded in January of last year by a trio of experienced entrepreneurs: Lewis Carhart, who serves as CEO, Claudio Fuentes as COO, and his brother Mariano Fuentes as CTO. The collaboration among the founders is rooted in a shared history of building technology ventures. Claudio and Mariano Fuentes have a nearly decade-long track record of co-founding startups, a partnership that predates their meeting with Carhart several years ago.
Their collective journey took a pivotal turn with LeapAI, a workflow platform they built together. Claudio served as CEO and co-founder, Carhart led growth initiatives, and Mariano was a senior full-stack engineer. LeapAI experienced considerable initial success, attracting over a million users within approximately two years. Despite its substantial user base, the team ultimately made the difficult decision to discontinue the platform. This closure was attributed to their inability to identify a "sticky enough use case to warrant continued investment," a crucial lesson in product-market fit.
However, the experience with LeapAI proved invaluable, serving as a fertile ground for the insights that would eventually give rise to Comp AI. The founders recounted that their time building LeapAI provided them with profound practical knowledge in several key areas. Firstly, they gained hands-on expertise in developing with Large Language Models (LLMs), understanding both their potential and the imperative of tailoring them to specific, high-impact applications. Secondly, and perhaps most critically for their future venture, they encountered firsthand the arduous and often opaque process of achieving SOC 2 compliance, particularly as they attempted to scale LeapAI to cater to larger enterprise clients.
SOC 2, or Service Organization Control 2, is an auditing procedure that ensures service providers securely manage data to protect the interests of their clients and the privacy of their customers. It is a critical certification for many businesses, especially those in the SaaS sector, as it demonstrates a commitment to security, availability, processing integrity, confidentiality, and privacy. For startups seeking to engage with larger enterprise customers, achieving SOC 2 compliance is often a non-negotiable prerequisite.
Claudio Fuentes vividly recalled the challenges, stating, "It’s a very obscure process. It took us a couple of months of doing things by hand, and the whole time it meant taking our eyes off building the product." This sentiment is widely echoed across the startup ecosystem, where founders often find themselves diverting scarce resources and valuable development time to manual compliance efforts, detracting from their core product roadmap. This firsthand frustration with the inefficiencies of traditional compliance methods ignited the spark for a new startup idea, one that directly addressed this pervasive pain point. This time, Lewis Carhart would take the helm as CEO, a natural progression given that the core concept for Comp AI originated from his insights into this market gap.
Comp AI’s Vision: Redefining Security and Compliance with AI Agents
Comp AI’s core offering is an agentic platform meticulously designed to tackle the often-tedious and labor-intensive work of security and compliance. In the context of AI, "agentic" refers to systems capable of understanding goals, planning actions, executing them, and adapting based on feedback, often autonomously or semi-autonomously. For Comp AI, this translates into AI agents performing a range of critical functions, from drafting comprehensive company security policies tailored to specific organizational needs to systematically collecting evidence required for security audits. Beyond discrete tasks, the platform also provides continuous monitoring capabilities, ensuring that a company consistently meets its established compliance controls in real-time.
This approach positions Comp AI at the forefront of the next generation of cybersecurity startups, which are leveraging advanced AI to help companies operate more efficiently and securely in what industry experts are increasingly calling the "agentic era." This era is characterized by the proliferation of intelligent software agents across various business functions, necessitating new paradigms for security and governance.
Lewis Carhart elaborated on the commercial imperative driving Comp AI’s solution in an interview with TechCrunch, stating, "For a lot of software companies, security and compliance are directly tied to revenue." He provided a common scenario: "a customer might ask a startup for a SOC 2 report before closing a deal." In today’s competitive landscape, a demonstrable commitment to security and compliance is not merely a regulatory obligation but a significant business differentiator and often a prerequisite for securing high-value contracts. Carhart emphasized, "What Comp AI automates is much of the work companies traditionally have to do around that process."
The global market for cybersecurity and compliance solutions is experiencing robust growth. Reports indicate that the global cybersecurity market size was valued at over $170 billion in 2023 and is projected to grow at a compound annual growth rate (CAGR) exceeding 13% through 2030, reaching well over $400 billion. Within this vast market, the compliance software segment alone is estimated to be worth tens of billions, driven by the ever-increasing complexity of regulations like GDPR, HIPAA, ISO 27001, and countless industry-specific mandates. This exponential growth underscores the pressing need for scalable, efficient, and intelligent solutions like Comp AI’s.
Crucially, the founders stress that while their software significantly streamlines the process of meeting and maintaining security requirements, it does not seek to replace the indispensable role of independent audit reviews or human oversight. The "human-in-the-loop" philosophy is central to Comp AI’s design. Human workers are vital for onboarding the AI systems, supporting and defining control parameters, and maintaining the overall agentic workflow. Carhart clarified this symbiotic relationship: "An agent might draft a policy, for example, but a person still reviews and approves it. As agents take on more consequential actions over time, we believe the level of safeguards and human approval should increase accordingly." This balanced approach acknowledges both the power of AI automation and the critical need for human judgment and accountability in sensitive areas like security and compliance.
Beyond compliance automation, Comp AI also offers AI-powered penetration testing. Carhart explained this advanced capability, noting that the platform "proactively tests codebases and infrastructures for vulnerabilities." Penetration testing, or ethical hacking, is a simulated cyberattack against a computer system, network, or web application to check for exploitable vulnerabilities. Integrating AI into this process allows for more frequent, thorough, and adaptive testing, potentially identifying weaknesses that might be missed by traditional, often manual, methods. The newly secured Series A capital is earmarked, in part, to fuel the expansion of these innovative product offerings, further solidifying Comp AI’s market position.
Addressing the New Frontier: Security Risks in the Agentic Era
The rise of agentic AI introduces a new wave of security risks that traditional, static compliance frameworks are ill-equipped to handle. The industry has seen a surge in discussions surrounding these novel threats, leading to the emergence of a new cohort of AI security and compliance companies, including established players like Vanta and Drata. Carhart articulates that the rapid adoption and experimental deployment of AI by companies are creating an urgent need for continuous – and perhaps even autonomous – security and compliance platforms.
He painted a vivid scenario to illustrate this challenge: "Imagine a company completes its SOC 2 audit and two weeks later deploys a new AI agent that can access customer data, change permissions across an internal system, or introduce a new vulnerability through code deployment. The audit didn’t become invalid; it simply wasn’t designed to tell you in real time what changed afterward." This example highlights a fundamental gap: traditional audits provide a snapshot in time, whereas modern, AI-driven environments are dynamic and constantly evolving. The agility of AI deployment outpaces the static nature of periodic compliance checks, creating windows of vulnerability and non-compliance.
Mariano Fuentes expanded on this critical need, emphasizing that as companies increasingly integrate AI, they must also possess the capability to demonstrate precisely "what an agent accessed, what it tried to do, and whether it stayed within the boundaries given." This demand for granular visibility and accountability is paramount for maintaining trust, ensuring data privacy, and mitigating risks associated with autonomous systems. Comp AI is directly addressing this by focusing on establishing robust permissions and accountability frameworks as a foundational layer. "We’re building toward a security layer that can monitor and validate those kinds of risk more continuously as these systems evolve," Mariano affirmed. This proactive and continuous monitoring capability is designed to provide real-time insights into AI agent behavior, ensuring adherence to security policies and compliance controls even as the systems themselves adapt and expand their functionalities.
Investor Confidence and Broader Market Implications
The substantial Series A investment from Roo Capital and Grand Ventures is a strong indicator of investor confidence in Comp AI’s vision and its potential to capture a significant share of the burgeoning AI-driven cybersecurity and compliance market. Investors are increasingly looking for companies that can solve critical, complex problems with innovative technology, and Comp AI fits this profile perfectly. The founding team’s prior experience, including the valuable lessons learned from LeapAI, likely played a crucial role in securing this funding, demonstrating resilience, adaptability, and a deep understanding of product development and market needs.
For the broader cybersecurity industry, Comp AI’s funding reinforces several key trends. Firstly, it underscores the accelerating shift from reactive security measures to proactive, continuous monitoring and automated remediation. Secondly, it highlights the increasing integration of artificial intelligence and machine learning across all facets of cybersecurity, from threat detection to compliance management. Finally, it signals that compliance is no longer just a cost center but an increasingly strategic business enabler, with efficient management becoming a competitive advantage. Companies that can demonstrate robust, continuous compliance are better positioned to win and retain clients in a trust-sensitive digital economy.
The market for AI governance and security is poised for exponential growth. As enterprises adopt more sophisticated AI models, the demand for tools that ensure these systems are secure, ethical, and compliant will only intensify. Comp AI’s early focus on "agentic" security and compliance positions it favorably to capitalize on this megatrend, offering solutions that are purpose-built for the complexities of an AI-first world.
Conclusion
Comp AI’s successful $34 million Series A funding round marks a significant milestone for the company and reflects a strong market belief in its innovative, AI-driven approach to cybersecurity and compliance. By addressing the tedious and often manual processes of security audits and policy enforcement with an agentic platform, Comp AI is poised to empower businesses to navigate the intricate landscape of regulations and emerging AI risks more efficiently and effectively. The company’s commitment to a human-in-the-loop philosophy, combined with its advanced capabilities in continuous monitoring and AI-powered penetration testing, positions it as a vital player in defining the future of enterprise security. As businesses continue their rapid adoption of AI, solutions like Comp AI’s will become indispensable for maintaining security, ensuring compliance, and ultimately, safeguarding revenue and reputation in the dynamic digital era.
About the Author